

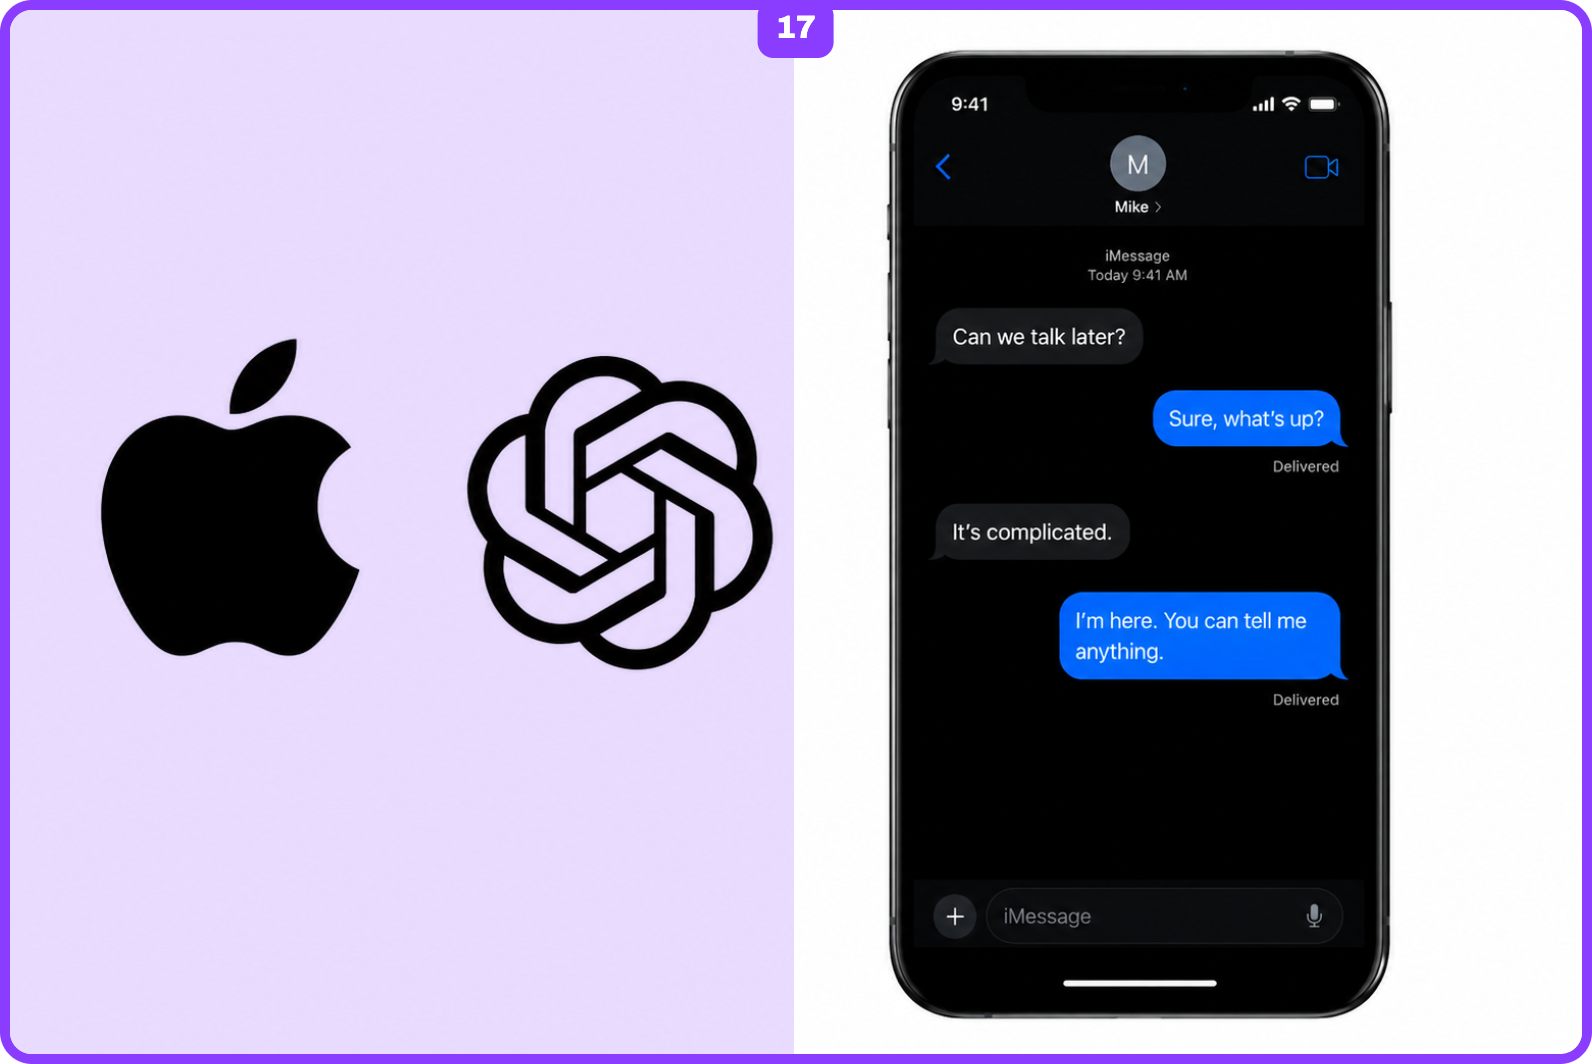
OpenAI released a plugin on 20 August 2026 that gives ChatGPT access to Apple Messages on a Mac. This is one of the most dangerous and irresponsible uses of AI because Apple Messages doesn’t just contain regular SMS. It contains end to end encrypted iMessages and supported encrypted RCS conversations between Apple and Android users.
The benefit
OpenAI is selling this as a way for ChatGPT to search chats, catch up on conversations, draft replies and send messages on your behalf. The plugin is available on every ChatGPT plan through the Mac desktop app, works inside ChatGPT Work and Codex, and requires an Apple silicon Mac.

It sounds incredibly useful, but I want to explain why the privacy costs and personal safety risks for high risk people outweigh the benefits. Convenience, security and privacy are always at odds, but this integration trades other people’s privacy for one person’s convenience.
I’ve included relevant experience at the end of this article for anyone who wants to know why I understand what this technology can access and what can be done with that access.
The cost
I explain further down why this is different from adding AI to scan email, or a telecom company or government accessing personal data.
People who rely on privacy accept that other forms of communication may be accessible to AI or third parties. That’s why they specifically choose Signal, Session, iMessage or supported encrypted RCS when privacy is required.
Someone can now give ChatGPT access to those conversations without telling the other participants or asking for their consent. They have no way of knowing it’s happening.
Unless that person tells every contact, someone can send information they’d never want shared with anyone else. OpenAI provides no indication to the other person that their conversation has a third party accessing it. By the time they send it, the disclosure has already happened.
The EU wants AI generated images and text labelled so people know AI was involved. This is one case where I’d advocate a label: people should be told when an AI company has been given access to their private conversation.
This affects people who never use ChatGPT
Anyone who sends an iMessage, SMS or supported encrypted RCS message to an Apple user can have that conversation exposed to ChatGPT if the recipient enables the integration on their Mac.
That includes Apple account holders using iMessage and Android users communicating with Apple users through SMS or supported RCS. They don’t need ChatGPT or an OpenAI account. They don’t even need an Apple device.
They only need to communicate with someone who has enabled the integration.
This risks private conversations with family, friends, doctors, lawyers, colleagues, political leaders, special operators, intelligence officers, whistleblowers, activists, journalists, customers and sources.


I wrote a preliminary warning on Twitter and LinkedIn as soon as I saw OpenAI’s announcement. Most people agreed with my concerns, but some don’t appreciate the difference between giving a third party full access to Apple Messages and integrating it with an operating system, software application or messaging service that isn’t end to end encrypted.
Why iMessage is different
Think Signal, not SMS.
Some people think of Apple Messages as ordinary text messaging, but it’s one application supporting 3 different messaging services: regular SMS, end to end encrypted iMessage and, more recently, RCS.
Many people specifically use iMessage because it provides end to end encryption comparable to Signal.
Integration with unencrypted services like SMS is less of a concern. The technology itself isn’t my objection. My concern is giving OpenAI access to a service people deliberately chose because they’re protected by end to end encryption.
I want to make one technical point absolutely clear because several people have misunderstood my argument:
The encryption still works.
OpenAI hasn’t cracked or mathematically broken iMessage encryption. An iMessage remains encrypted between endpoints.
The privacy problem occurs at the endpoint. Once the message has been decrypted on the recipient’s Mac, that recipient can authorise third party software to access the readable conversation.
The encryption worked exactly as designed. It simply can’t protect message content from software authorised to access it before or after decryption.
That’s what I mean when I say this integration undermines the purpose of end to end encryption.
Adding this ChatGPT plugin to Apple Messages is like installing spyware that can be exploited by governments, intelligence agencies, law enforcement, internal threat actors at OpenAI and partners. It introduces invasive client side monitoring directly inside a messaging app, exposing message content where end to end encryption can no longer protect privacy.
What is end to end encryption?
End to end encryption is the most secure way to communicate because only the sender and intended recipient can read the message. Content is encrypted on the sender’s device before it’s sent and remains encrypted while travelling through networks and servers.
It can be intercepted in transit by hackers, intelligence agencies or the company operating the service, but can’t be read without the encryption keys or access to the message before encryption or after decryption.
Even the service provider can’t read the message content. With iMessage, that’s Apple.
When the FBI tried to force Apple to bypass iPhone security, Apple refused because creating a way around encryption would create a backdoor that couldn’t be guaranteed for government use alone.
Apple said the only way to guarantee such a capability isn’t abused or obtained by the wrong people is never to create it. Apple also warned that weakening encryption puts both privacy and personal safety at risk.
Why governments want access
In 2013, Edward Snowden revealed US intelligence agencies had built surveillance programs collecting communications at scale.
NSA programs including PRISM exposed government access to internet communications, while Section 215 enabled bulk collection of telephone metadata, including records from telecom networks like Verizon.
That metadata allowed intelligence agencies to analyse who communicated with whom, when and how frequently.
Conversation content can reveal considerably more. It can explain who those people are, how they know each other, where they go, who they work with, what they discuss and why they’re communicating.
Governments can intercept encrypted traffic, but they can’t simply read messages sent through Signal, Session or iMessage because those services use end to end encryption.
The FBI calls this “Going Dark” because encryption can prevent law enforcement from obtaining readable communications even when it has legal authority to demand information from the provider.
Governments, particularly the Five Eyes nations of the US, UK, Australia, Canada and New Zealand, have pushed for access to encrypted communications for years, citing terrorism, serious crime, national security and, more recently, child safety.
Why ChatGPT is like a backdoor
ChatGPT gives governments and law enforcement another route to information they’ve wanted for years, except people voluntarily enable the access themselves.
The plugin gives ChatGPT access to readable message content at the endpoint, before encryption for outgoing messages or after decryption for incoming messages, bypassing the privacy provided by end to end encryption while messages are transmitted between participants, without forcing Apple to build a cryptographic backdoor.
One person can expose conversations involving many people they communicate with. Information subsequently processed or retained by OpenAI can become subject to US legal process.
Calling this an endpoint security or operational security issue describes where the exposure occurs. It doesn’t remove the privacy consequence for participants who never authorised the access.
Apple didn’t create a new iMessage API for ChatGPT
OpenAI didn’t need Apple to create a new iMessage API.
The plugin uses existing macOS capabilities and requires the Mac owner to grant permissions including Full Disk Access, Contacts and Automation.
Apple has long warned customers about the amount of information exposed by Full Disk Access and specifically identifies Messages among the private data that applications may be able to access.
That capability existed before ChatGPT.
My concern is that OpenAI has now turned existing macOS access into a consumer AI feature specifically designed to read, search and act on Apple Messages.
I doubt these permissions were originally designed around the expectation that consumers would deliberately give a third party access to years of private conversations. They predate modern AI agents capable of searching, analysing and extracting information from large amounts of unstructured text.
Local plugin, remote AI
OpenAI says the plugin works locally and doesn’t build a complete message index.
I’m not claiming OpenAI uploads the entire Messages chat.db database to its servers.
Local plugin execution and local AI processing are 2 different things.
When ChatGPT uses an OpenAI hosted model to summarise a conversation, analyse it or draft a reply using its contents, the information required for that request must be available to the hosted model for processing.
What OpenAI retains depends on the account, product and settings.
Processing and retention are also different. I’m not claiming every message ChatGPT accesses is permanently stored by OpenAI.
My concern begins when content previously protected by end to end encryption becomes available to a third party for processing without every participant knowing or consenting.
As Proton put it on X:
OpenAI says it runs locally and doesn't build an index. Local execution isn't the same as local processing. The moment ChatGPT summarises a thread or drafts a reply using a hosted model, that content leaves the machine.
US law makes information OpenAI possesses accessible
Under US law, OpenAI must preserve data covered by valid preservation orders and disclose customer content and records when legally compelled.
The CLOUD Act can apply to data within a US provider’s possession, custody or control regardless of where that data is physically stored.
Moving data from US servers to an EU country therefore doesn’t put it beyond US legal process if OpenAI retains possession, custody or control.
OpenAI can also be legally prohibited in some circumstances from telling the affected customer that information has been preserved or disclosed.
A dangerous example
Imagine a whistleblower chooses iMessage to communicate privately with an investigative journalist. The journalist enables ChatGPT. The whistleblower hasn’t consented and isn’t notified.
Content from their private conversation can now be processed by OpenAI without the whistleblower’s knowledge. Information OpenAI subsequently retains can become exposed to government demands, account compromise, security vulnerabilities and data breaches.
Sam Altman has said OpenAI can be forced to produce people’s sensitive ChatGPT conversations and called the absence of legal confidentiality “very screwed up”.
In 2025, a US court ordered OpenAI to preserve ChatGPT conversations as evidence in The New York Times copyright lawsuit, including some conversations users had deleted.
The journalist authorised ChatGPT’s access. The source didn’t.
I doubt a responsible investigative journalist would knowingly do this because source protection is fundamental to their work. But the example demonstrates the privacy consequence for anyone communicating with someone who enables the integration.
“Anyone can screenshot your messages”
This has been my favourite response on Twitter.
Yes, someone can screenshot your messages and fax them to the FBI. That’s deliberate disclosure by a participant. Giving a third party access to automatically read, search and analyse private conversations involving people who never consented is a different privacy risk.
“The recipient could always share your messages”
Correct.
A recipient has always been able to copy, forward, export or deliberately disclose a message. That doesn’t mean automating third party access to potentially years of conversations doesn’t create additional privacy risk.
“Any Mac app with Full Disk Access could already do this”
Correct.
Apple specifically warns customers about the access Full Disk Access provides. That existing capability is part of my concern, not a rebuttal to it. OpenAI didn’t invent endpoint access. It has productised and normalised third party AI access to Apple Messages for ordinary consumers.
Agents, coding tools and other applications with equivalent access deserve the same attention. I’ve already written about the risks of giving AI broad access to computers and critical applications.
“This is no different from email, SMS, Slack or Teams”
It is.
Think Signal, not SMS.
SMS, ordinary email, Slack and Teams don’t provide the same promise of privacy as iMessage, Signal, or Proton, where the service is designed so the provider itself can’t read the end to end encrypted message content.
I have concerns about giving AI access to email, browsers and entire computers too. I’ve written about them already.
💡 My objection here is specifically about introducing third party AI access to communications people deliberately chose because of the privacy provided by end to end encryption.
“I opted in, so it’s not a problem for me”
You opted in. Everyone you communicate with didn’t.
That is the fundamental privacy problem.
One person makes the decision. Potentially hundreds of other people experience the consequence without being asked or notified.
The network effect
One person enabling this integration can expose accessible conversations involving dozens or hundreds of other people. At scale, those conversations overlap.
One ChatGPT customer can expose conversations involving many non customers and chose specifically not to allow AI access to their private communications. Those people communicate with other people. Group conversations connect multiple participants simultaneously.
Names, phone numbers, email addresses, timestamps, Contacts information and message content can provide enough information to identify people and relationships between them. If this capability becomes widely adopted, and I believe it will unless Apple puts a stop to it, the privacy consequence extends beyond the number of people who actually enable it.
Private conversations can reveal a social graph
Snowden’s disclosures demonstrated how useful telecom metadata can be for analysing relationships. Message content can provide more context about those relationships.
Imagine years of conversations establish that Sarah works at Company X, is married to John, lives in San Francisco, travelled to Washington last month and regularly discusses a confidential project with James.
Those facts don’t need to exist together in one database record. AI can extract information distributed across conversations and connect it. Across enough conversations, that can identify family members, friends, colleagues, employers, customers, doctors, lawyers, journalists, sources and other relationships.
Group conversations can expose connections between several people simultaneously.
Messages can contain locations, travel plans, meetings, photographs, documents, financial information, medical information, legal discussions, account information, authentication codes, political opinions, intimate relationships, disputes and confidential business information.
I haven’t seen evidence that OpenAI automatically constructs and permanently stores a social graph from Apple Messages, so I’m not claiming it does.
I’m worried that’s what becomes technically possible when AI can process readable conversations. Enough private messages can reveal who someone is, who they know, where they’ve been, who they work with, who they trust, what they discuss and how those people are connected.
The people being identified don’t need ChatGPT. They only need to appear in conversations accessible to ChatGPT on someone else’s Mac.
The UK government demonstrated why this is important
In 2025, the UK government demanded access to iCloud data protected by Apple’s Advanced Data Protection.
Because end to end encryption prevented Apple from decrypting the protected data, the government demanded access. Apple refused and withdrew ADP for UK customers instead.
This also addresses another argument people have made about iCloud.
Without Advanced Data Protection, Apple can hold keys needed to recover certain iCloud data, and the protection of Messages in iCloud also depends on how iCloud Backup is configured. That’s a legitimate privacy concern. But the existence of one route to information doesn’t justify creating another.
💡 The UK government’s attempt to obtain access to ADP protected data demonstrates exactly why some people deliberately choose end to end encryption.
Adding another company to the readable conversation creates another route to information Apple designed itself not to possess in readable form under end to end encryption.
It can access security codes
Apple Messages also contains SMS, MMS and RCS messages forwarded from an iPhone to a Mac. That can include one time authentication codes from banks, email accounts and other services. With Messages in iCloud enabled, SMS history can also be synchronised across devices.
What the permissions give ChatGPT
ChatGPT requires powerful macOS permissions to work with Messages, including Full Disk Access, Contacts and Automation.
Those permissions can allow it to read message content and attachments, associate conversations with participants and interact with Messages. It asks for approval before sending, but approval can be switched off per conversation, and that approval relates to outgoing actions.
By the time ChatGPT can use the contents of a conversation to help with a request, it must have access to the information required to perform that task. Most people won’t realise how much historical information may exist on their Mac.
💡 With Messages in iCloud enabled, years of message history can be accessible, including conversations and attachments synchronised through iCloud.
Two wrongs don’t make a right
I’ve consistently warned against integrating AI with critical systems like email or giving it full computer control because the risks are substantial and always will be. The fact that people already enable other dangerous integrations doesn’t justify giving OpenAI access to end to end encrypted messages.
The fact that another application could already access information with sufficient permissions doesn’t make this implementation harmless.
The fact that another participant could deliberately disclose your messages doesn’t make automated third party access equivalent.
Capability is not justification.
Trusting OpenAI means trusting everyone OpenAI trusts
Giving OpenAI access means trusting Sam Altman and the company’s infrastructure, employees, partners, vendors, security, retention practices and legal obligations. That includes Tel Aviv based security testing company Irregular, formerly Pattern Labs.
In August 2026, OpenAI confirmed its models weren’t contained by properly configured sandbox environments. During testing by security firm Irregular, a misconfiguration allowed its models to access the internet and exploit a real website.
Separately, OpenAI models “escaped” an internal testing environment, accessed the internet and breached Hugging Face, while also accessing vulnerable customer infrastructure hosted by Modal Labs. OpenAI doesn’t need to act maliciously for private information to be exposed.
Imagine if OpenAI, an employee, vendor or partner did.
I’m not saying they would.
I’m saying more than 1 billion people could communicate with people who have enabled this integration and have no way of knowing they’re trusting OpenAI and its partners with information from their conversations, regardless of who they are, where they are or what they’re discussing.
🛑 Do not give ChatGPT access to Apple Messages.
Even if you’re comfortable with the privacy consequences, the people you text might not be.
Why listen to me?
I built some of the first messaging chatbots. I wouldn’t build this for my customers.
I’m including specific information about my background because my analysis isn’t limited to what OpenAI says the plugin does or what Apple documents in its developer materials. My experience across messaging, chatbots, telecom infrastructure, mobile operating systems, browsers, APIs and lawful interception means I look at what the technology is capable of doing once access is granted, including capabilities that may never appear in a press release or product description. That’s important when assessing privacy and security risk.
Between 2015 and 2018, I spoke at developer conferences about chatbot integrations and built the world’s first security chatbots for major messaging services including HipChat, Slack, Messenger, Skype and Telegram. MetaCert’s was listed among Slack’s top 20 chatbots for 2 years.
That experience meant I understood early how much information messaging integrations could expose once a user granted access, including information belonging to people who never installed the integration or consented to it. I was evaluating what the permissions made technically possible, not just what developers said their chatbots were designed to do.
My experience with messaging goes much further back.
I helped launch AIM in 1997, one of the first mass market consumer messaging services on the Internet. I later founded a telecom testing company and led major SMS and MMS infrastructure projects during the 2000s.
I also conducted a technical audit of NewNet, now part of SS8, whose technology provides lawful interception capabilities to telecom operators and intelligence agencies worldwide.
My teams have built custom Android firmware and complete browsers for iOS.
I’ve worked across messaging infrastructure, mobile operating systems, browsers, APIs, permissions and the information those technologies expose.
My team built a CRM platform for the emerging chatbot developer community in 2016. Slack’s original API exposed extraordinary amounts of information, including personal contact details and locations for people inside organisations that installed a chatbot. Our CRM connected that information to individual people and their organisations.
I know what’s technically possible and what it costs in privacy.
I also built a simple news reputation chatbot for Messenger in 2017, used by journalists, including at Al Jazeera. They pasted a URL for a story or video, and it identified whether the website or social media account was classified as disinformation, far left, far right, satire or mainstream.
I was teaching developers how to build messaging integrations and advocating for ethical design years before ChatGPT made conversational AI mainstream.
I don’t just investigate what developers say their technology does. I look at what the technology can do, what information it can access and what can happen when those capabilities are deployed at scale.
Most leading security vendors license my portfolio of patents for in app security so they can protect people from malware and phishing. The portfolio covers 65 categories, including child safety and child abuse.
This means I spotted potential threats with how apps would eventually open links inside an app WebView instead of the native browser before app developers themselves knew it would become a problem, never mind Gartner analysts or consumers.
If the EU forces technology companies to add monitoring to their apps through “Chat Control” 2.0 under the guise of online child abuse protection and anti grooming, Signal would have to ask me for permission before scanning links inside messages prior to encryption. I’m not willing to license patents if it means breaking the privacy purpose of end to end encryption so governments can introduce client side surveillance.
My position is consistent with concerns Signal President Meredith Whittaker has repeatedly raised about client side scanning of encrypted communications.
I’m giving Signal and other ethical companies a get out of jail free card because they don’t want to add spyware to their apps.
⛔️ Based on my experience, which is much more extensive than what I’ve mentioned here, this OpenAI integration should concern people.
It should concern Apple.
I wouldn’t build any security service for iMessage or Signal if it required access to readable conversations because the security benefit wouldn’t justify the loss of privacy provided by end to end encryption.
Transparency statement
I have a commercial interest in this subject and readers deserve to know.
I founded MetaCert, and our Link Verifier is launching in the US with Mackie Mobile, a veteran owned wireless carrier built for people who need privacy and security by default: special operators, law enforcement, government personnel and anyone who doesn’t want their identity, location or data collected and sold.
Mackie Mobile subscriptions also include prvc, a peer to peer messaging service designed to be more private than iMessage and Signal. Its developers have been working on the technology for years, and we’ve been beta testing it for the past 9 months. Link Verifier works with it through the same user initiated process. Nothing reads conversations before encryption or after decryption, so it doesn’t undermine the privacy this article defends.
The commercial interest doesn’t change the design difference at the centre of this article. ChatGPT needs access to conversations to provide these features.
If anything in this piece is factually incorrect, I want to know. Please get in touch and I’ll correct it promptly.
Nothing written here is intended as a legal accusation or assertion of wrongdoing. All statements are based on publicly available information and my own analysis and opinion.
Why subscribe?
Subscribe to get full access to 1 weekly newsletter and full archive.
Stay up-to-date
Be part of a community tracking surveillance tech, new laws and the people in power dismantling everyone’s right to privacy, digital safety and online anonymity. I also write about cybercrime.
Create a Substack account to join the discussions and get notified as I publish. I write as stories break, so you know what’s happening while it’s happening.
What I write about
In 1996, before the web went mainstream, I wrote one of the first newsletters on the Internet. I built a community of 9,000 AOL beta testers to introduce new technologies, gather feedback and help launch products like AIM, the first mainstream consumer internet messaging service.
Today, I analyse and explain what new technology, AI and legislation is doing to society under the guise of “public safety”, “child protection” and “national security”.
Why Substack
Enough LinkedIn readers asked me to create a Substack, so I did. My posts rank in the top 0.5% for readership and engagement, but LinkedIn restricted my account 3 times as engagement grew around posts analysing and critiquing powerful people like Larry Ellison, tech companies such as Palantir, political leaders including Ursula von der Leyen, intelligence agencies such as Israel’s Unit 8200, and government policies like “Chat Control”.
I’m moving my work here so it has a permanent home beyond algorithm control.
Expect 5 to 10 short, information loaded posts a week without the jargon. I might publish 3 in one day, then nothing for a couple. Most stay within LinkedIn’s 3,000 character limit. Once a month, I’ll go deeper with a longform investigation.